A Practical Guide to ISO 27001 Readiness
Many organisations assume ISO 27001 certification is only for large enterprises. In reality, businesses of all sizes can benefit from implementing an Information Security Management System (ISMS).
Whether you’re pursuing certification to win contracts or improve security, preparation is key.
Understand the Standard
ISO 27001 provides a framework for managing information security risks.
It’s not simply an IT project—it involves people, processes and technology working together.
Identify Your Information Assets
Start by understanding what information your organisation holds.
This may include:
- Customer records
- Employee data
- Financial information
- Intellectual property
- Supplier information
Knowing what you need to protect is the foundation of effective security.
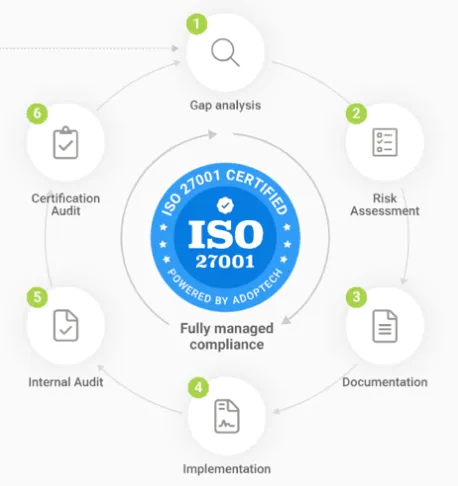
Perform a Risk Assessment
Identify:
- What could happen?
- How likely is it?
- What would the impact be?
This allows you to prioritise investment where it matters most.
Document Policies
ISO 27001 requires documented policies covering areas such as:
- Access control
- Incident management
- Asset management
- Acceptable use
- Backup and recovery
These should reflect how your business actually operates.
Build a Security Culture
Technology alone won’t achieve certification.
Staff awareness training, clear responsibilities and management commitment are all essential.
Before Certification
Conduct an internal audit and management review before engaging a certification body.
Addressing gaps early saves time, money and stress during the formal assessment.
Final Thoughts
ISO 27001 isn’t just about achieving a certificate—it helps organisations reduce risk, improve governance and demonstrate security maturity to customers.