About KH-InfoSec
Security advice from people who’ve sat where you sit.
We started KH-InfoSec because too many growing businesses were being sold fear, jargon and oversized retainers instead of straightforward, proportionate security advice.
Our mission
To make enterprise-grade security leadership accessible to every growing organisation — in plain English, at a fair price, without the scare tactics.
Our approach
We start with your business, not a checklist. Every recommendation is weighed against your risk, budget and growth plans — then delivered as a roadmap your board can actually follow.
Our Team
A short introduction to your team members and why their backgrounds should inspire potential clients’ confidence.

Keith Hickson (Director)
As a seasoned Information Security and Data Protection consultant based in Oxfordshire, I specialize in helping organizations strengthen their cybersecurity posture to win and maintain contracts with enterprise organizations. Through my work with global leaders like Fujitsu Services, PwC, and Hewlett Packard Enterprise, I've played a key role in securing multi-million-pound contracts, including; A data centre outsource bid for a global bank valued at €3 billion. Renewal contracts for provision of health insurance policy administration services valued at £75m. An end user computing and service desk bid valued at £100m.
Phil Byrne
Phil is a long standing member and current Chair of the NSAI Quality Management Standards Committee. This gives Phil a significant advantage in the Compliance & ISO consultancy community, representing the interests of Irish businesses in relation to the application and evaluation of the ISO Suite of Technical and Management Systems Standards. He is also a member of a number of National and International working groups including: Governance of Organisations; Internal Investigations; Managing Emerging Risk; and Human Trafficking, Forced Labour & Modern Slavery.
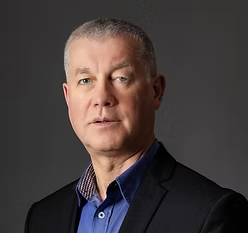
Vincent Delany
As Consultant Lead Auditor for ISO Management Systems Standards, with extensive experience throughout his career in people and process management, Vincent has worked in many sectors, helping management teams improve how they plan, resource and operate their businesses, with the primary objective being: to maintain conformance to the Subscribed Standards and applicable legislation and regulations, including EU/UK-GDPR.
Why clients trust us
Straightforward, independent, accountable.
No products to sell
Our advice isn’t tied to any vendor or software — we recommend what’s right for you.
Board-ready reporting
Every engagement produces reporting your leadership team can actually use.
Long-term partners
Most clients keep us on retainer well beyond their first certification.
Frequently asked questions
Questions we hear often.
How is a Fractional CISO different from an IT provider?
An IT provider manages your systems and technical security. A Fractional CISO sets strategy, manages risk, compliance, and reports to your board — independent of who runs your IT.
How quickly can we get started
Most engagements begin within a week of your discovery call..
Do you work with businesses that have no security function today?
Yes — that’s most of our clients when we start working together.
Can you help with a specific audit or certification deadline?
Yes, our Individual Security Projects and Certifications services are built for exactly this.